Dynamic Tool Loading
Built-in tools (bash, read, edit, …) are always available. MCP tools are loaded on demand so that connecting a server with hundreds of tools doesn’t flood the model’s context. Four tools drive this.
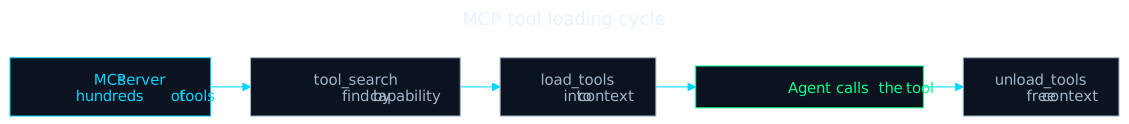
The Loading Tools
| Tool | Purpose |
|---|---|
tool_search | Find MCP tools by capability (query, optional limit) |
load_tools | Load specific tools into the active context |
unload_tools | Remove loaded tools to free context |
list_loaded_tools | Show which tools are currently loaded |
The agent uses these automatically: it searches for a capability, loads the matching MCP tool, calls it, and can unload it afterward.
tool_search
{ "query": "sql injection testing", "limit": 10}Returns matching MCP tools with their descriptions. Built-in tools don’t need searching — they’re always callable.
What’s Lazy vs Always-On
- Always available — every built-in tool (
bash,read,edit,glob,grep,write,task,webfetch,websearch, memory tools, …). - Loaded on demand — tools exposed by connected MCP servers (including Bolt). They are discovered with
tool_searchand pulled in withload_tools.
Disabling a Tool
The tools config is a map of tool name → boolean. Set a tool to false to disable it:
{ "tools": { "websearch": false }}Related Documentation
- Tools Overview - All built-in tools
- Bolt / MCP - Connecting MCP servers
- Configuration - Tool settings