Tools Reference
Cyberstrike provides a comprehensive set of built-in tools for security assessments. These tools enable file operations, command execution, web automation, and persistent memory across sessions.
📸 SCREENSHOT: s11-tool-list.png
Tool listesi - TUI’da mevcut araçların görünümü
Tool Categories
| Category | Tools | Purpose |
|---|---|---|
| File Operations | Read, Write, Edit, Glob, Grep | File reading, writing, editing, and searching |
| Command Execution | Bash | Shell command execution |
| Web Testing | Hacker Browser | Autonomous crawler with traffic capture |
| Memory | Memory Search, Memory Write, Memory Read, Memory Context | Persistent storage across sessions |
| Tool Discovery | ToolSearch, LoadTools, UnloadTools | Dynamic MCP tool loading |
| Tasks | Task, TodoWrite | Delegation and task tracking |
| Web | WebFetch, WebSearch, CodeSearch | Web content fetching and search |
File Operations
Read
Reads file contents with line numbers. Supports text files, images, and PDFs.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
filePath | string | Yes | Path to the file (absolute or relative) |
offset | number | No | Line number to start from (1-indexed) |
limit | number | No | Number of lines to read (default: 2000) |
Example
{ "filePath": "/path/to/file.txt", "offset": 100, "limit": 500}Output Format
00001| First line of content00002| Second line of content00003| Third line of content
(End of file - total 3 lines)
Features
- Automatic binary file detection
- Image and PDF support (returns base64 encoded content)
- Line truncation at 2000 characters
- Maximum 50KB per read operation
- Smart file suggestions on not found errors
Write
Creates or overwrites a file with new content.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
filePath | string | Yes | Absolute path to the file |
content | string | Yes | Content to write |
Example
{ "filePath": "/path/to/new-file.txt", "content": "File contents here"}Features
- Creates parent directories if needed
- Generates unified diff for review
- LSP diagnostics after write
- File time tracking for conflict detection
Edit
Performs find-and-replace operations on files with smart matching.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
filePath | string | Yes | Absolute path to the file |
oldString | string | Yes | Text to find and replace |
newString | string | Yes | Replacement text |
replaceAll | boolean | No | Replace all occurrences (default: false) |
Example
{ "filePath": "/path/to/file.ts", "oldString": "function oldName(", "newString": "function newName(", "replaceAll": false}Smart Matching
The Edit tool uses multiple matching strategies:
- Simple Replacement: Exact string match
- Line Trimmed: Ignores leading/trailing whitespace per line
- Block Anchor: Matches first and last lines, fuzzy middle
- Whitespace Normalized: Collapses multiple spaces
- Indentation Flexible: Ignores indentation differences
- Escape Normalized: Handles escape sequences
- Context Aware: Uses surrounding context for matching
Features
- Unified diff generation
- LSP diagnostics after edit
- Multiple occurrence detection
- Conflict prevention via file time tracking
Glob
Finds files matching a glob pattern.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
pattern | string | Yes | Glob pattern (e.g., **/*.ts) |
path | string | No | Directory to search (default: current directory) |
Example
{ "pattern": "**/*.{ts,tsx}", "path": "/path/to/project"}Output
Returns file paths sorted by modification time (newest first), limited to 100 results.
Pattern Examples
| Pattern | Matches |
|---|---|
*.ts | TypeScript files in current directory |
**/*.ts | TypeScript files recursively |
src/**/*.{ts,tsx} | TS/TSX files in src directory |
!**/node_modules/** | Exclude node_modules |
Grep
Searches file contents using regex patterns. Built on ripgrep.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
pattern | string | Yes | Regex pattern to search |
path | string | No | Directory to search (default: current directory) |
include | string | No | File pattern filter (e.g., *.js) |
Example
{ "pattern": "password|secret|api_key", "path": "/path/to/project", "include": "*.{js,ts,py}"}Output Format
Found 5 matches
/path/to/file.ts:  Line 42: const apiKey = process.env.API_KEY  Line 85: // TODO: remove hardcoded secret
/path/to/config.js:  Line 12: password: "changeme"
Features
- Regex support (ripgrep syntax)
- Hidden file search
- Symlink following
- Results sorted by modification time
- Maximum 100 results
Command Execution
Bash
Executes shell commands with timeout and output capture.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
command | string | Yes | Command to execute |
timeout | number | No | Timeout in milliseconds (default: 120000) |
workdir | string | No | Working directory |
description | string | Yes | Brief description of command purpose |
Example
{ "command": "nmap -sV -sC target.com", "timeout": 300000, "workdir": "/path/to/project", "description": "Scan target for open ports and services"}Features
- Shell detection (bash/zsh/sh)
- Process tree killing on timeout
- Permission system integration
- Real-time output streaming
- External directory access control
Security Considerations
Commands are parsed with tree-sitter to detect:
- Directory access outside project
- Dangerous command patterns
- File system modifications
Web Testing
There is no low-level Browser tool. Browser-based web testing is driven by the Hacker Browser — an autonomous crawler that logs in, walks the application, and captures traffic for the proxy testing pipeline.
🎬 GIF: g06-browser-scanning.gif
Hacker Browser crawling a target (25s)
Launch it with cyberstrike hackbrowser <target> or the hackbrowser tool. See Hacker Browser for the full workflow, and Web Testing for how the captured traffic is tested.
Memory System
Cyberstrike includes a persistent memory system for storing context across sessions.
Memory Write
Stores information to persistent memory.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
content | string | Yes | Content to store |
type | string | No | long_term for MEMORY.md, daily for dated notes |
title | string | No | Optional heading for the entry |
Example
{ "content": "Target uses PostgreSQL 14.2 on port 5432", "type": "long_term", "title": "Database Configuration"}Memory Types
| Type | Storage | Purpose |
|---|---|---|
long_term | .cyberstrike/MEMORY.md | Decisions, preferences, important facts |
daily | .cyberstrike/memory/YYYY-MM-DD.md | Session notes, temporary context |
Memory Search
Searches through stored memory.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
query | string | Yes | Search keywords or phrases |
Example
{ "query": "database credentials"}Memory Read
Reads specific memory files.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
file | string | Yes | File identifier |
File Identifiers
| Identifier | Description |
|---|---|
long_term | Long-term memory (MEMORY.md) |
today | Today’s daily notes |
yesterday | Yesterday’s notes |
YYYY-MM-DD | Specific date’s notes |
list | List all memory files |
Memory Context
Retrieves full memory context for the session.
Parameters
None required.
Example
{}Returns combined long-term memory and recent daily notes.
Dynamic Tool Loading
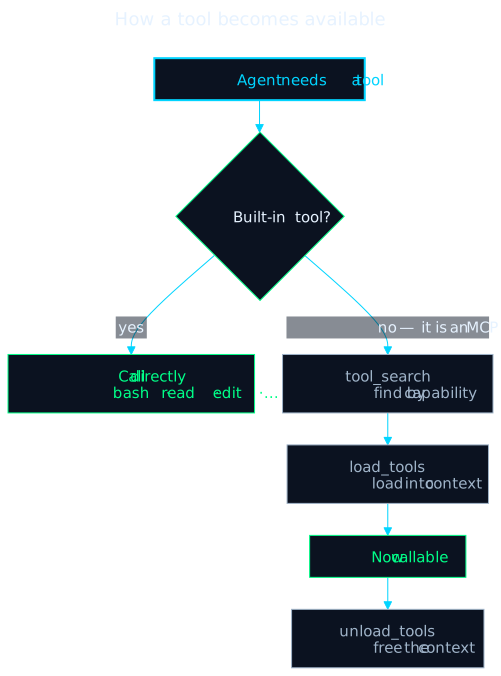
Cyberstrike supports dynamic tool loading for MCP (Model Context Protocol) servers. This enables access to hundreds of tools without overwhelming the context window.
Tool Search
Searches available MCP tools by capability.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
query | string | Yes | Capability description |
limit | number | No | Maximum results (default: 5) |
Example
{ "query": "sql injection testing", "limit": 10}Output
Found 3 tools:
1. sqlmap_scan   SQL injection scanner using sqlmap   Estimated tokens: ~500
2. nuclei_sqli   Nuclei templates for SQL injection   Estimated tokens: ~300
3. manual_sqli   Manual SQL injection payloads   Estimated tokens: ~200
Load Tools
Loads tools into context for use.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
tool_ids | string[] | Yes | Tool IDs from search results |
Example
{ "tool_ids": ["sqlmap_scan", "nuclei_sqli"]}Unload Tools
Removes tools from context to free budget.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
tool_ids | string[] | Yes | Tool IDs to unload |
List Loaded Tools
Shows currently loaded tools and token usage.
Parameters
None required.
Task Management
Task
Delegates work to a subagent. This is how the primary agent dispatches specialized subagents (see Agents).
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
description | string | Yes | A short (3-5 word) task description |
prompt | string | Yes | The task for the subagent to perform |
subagent_type | string | Yes | Which subagent to dispatch (e.g. web-application, general) |
TodoWrite
Writes task items to a todo list.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
tasks | array | Yes | Array of task objects |
Task Object
{ "id": "1", "content": "Scan for open ports", "status": "pending", "priority": "high"}Web Tools
WebFetch
Fetches and processes web content.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
url | string | Yes | URL to fetch |
format | string | No | text, markdown, or html |
timeout | number | No | Timeout in seconds (max 120) |
Example
{ "url": "https://target.com/robots.txt", "format": "text"}WebSearch
Performs web searches for information gathering.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
query | string | Yes | Search query |
CodeSearch
Searches code repositories and documentation.
Parameters
| Parameter | Type | Required | Description |
|---|---|---|---|
query | string | Yes | Code search query |
Tool Permissions
Each tool requires specific permissions that can be configured:
| Permission | Tools | Default |
|---|---|---|
read | Read | ask |
edit | Write, Edit | ask |
glob | Glob | allow |
grep | Grep | allow |
bash | Bash | ask |
websearch | WebSearch | ask |
webfetch | WebFetch | ask |
codesearch | CodeSearch | ask |
task | Task | ask |
external_directory | Access outside the project | ask |
Configuration
{ "permission": { "bash": "ask", "edit": "allow", "read": "allow", "glob": "allow", "grep": "allow" }}Permission Actions
| Action | Description |
|---|---|
ask | Prompt user for approval |
allow | Auto-approve without asking |
deny | Block tool usage |
See Permissions for the full model and glob patterns.
Creating Custom Tools
Add custom tools by creating files in .cyberstrike/tools/:
import { z } from "zod"
export default {  description: "Custom vulnerability scanner",  args: {    target: z.string().describe("Target URL to scan"),    depth: z.number().default(3).describe("Scan depth"),  },  async execute(args, ctx): Promise<string> {    const { target, depth } = args    // Custom scanning logic    return `Scanned ${target} to depth ${depth}`  },}
Files in a tool/ or tools/ directory inside any .cyberstrike/ folder are loaded automatically.
Tool Definition Schema
| Field | Type | Description |
|---|---|---|
description | string | Tool description shown to the model |
args | object | Map of parameter name → Zod schema |
execute | function | async (args, ctx) => string |
MCP Server Tools
Cyberstrike can load tools from MCP servers. The recommended approach is Bolt, which provides security tools through a Docker container with a plugin system:
{ "bolt": { "local": { "url": "http://localhost:3001", "enabled": true } }}MCP tools become available as direct tool calls — each plugin is called directly by name (e.g., nmap, nuclei, ffuf).
Tip
See Bolt for the recommended security-tools setup — 7 plugins plus ~26 aggregated MCP servers, all available as direct tool calls.